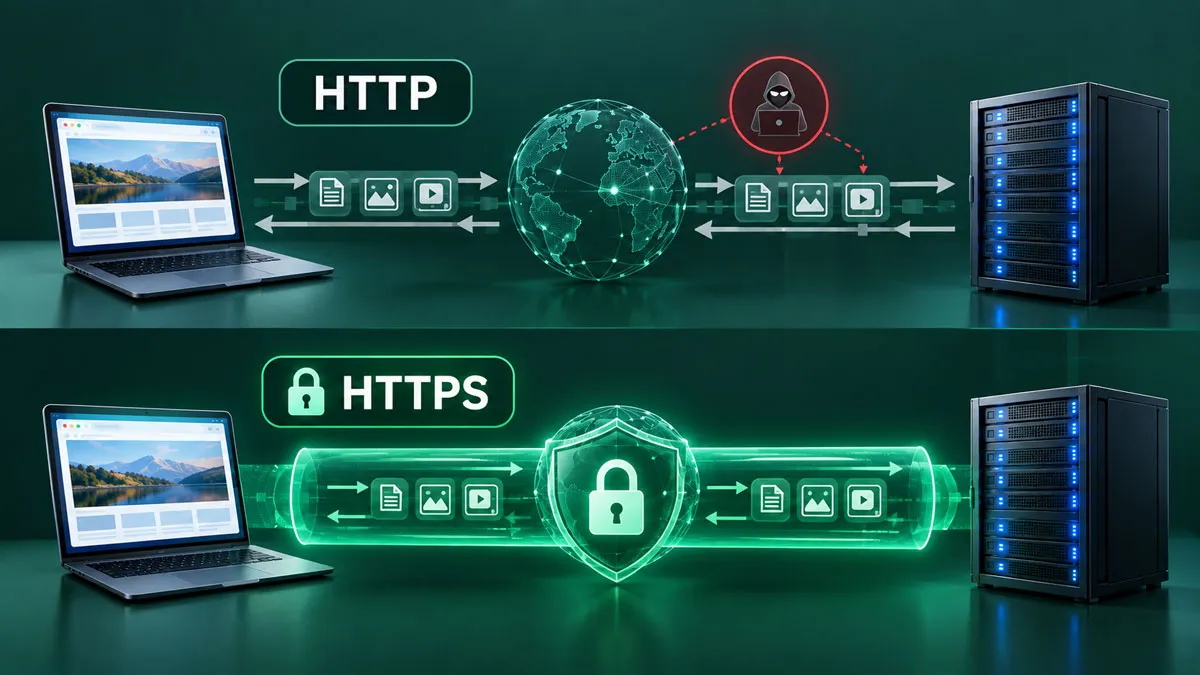
Every time a browser loads a webpage, sends information to a server, or retrieves an image, a communication protocol is working in the background. HTTP provides the rules for exchanging information between clients and servers, while HTTPS adds a protected communication layer using Transport Layer Security (TLS).
Understanding the difference matters because HTTP describes how web communication works, whereas HTTPS provides additional protection for information traveling between a client and a server.
What Is HTTP?
HTTP stands for Hypertext Transfer Protocol. It is an application-layer protocol used to exchange resources across networks, including HTML documents, images, videos, scripts, and data used by web applications.
HTTP follows a client-server model. A client, such as a web browser, sends a request to a server. The server processes that request and sends back a response. HTTP is also stateless, meaning that the protocol itself does not require the server to retain information about previous requests.
How An HTTP Request Works
A typical exchange begins when a browser requests a resource. The request can specify what the client wants and can include additional information through HTTP headers. The server then returns a response containing information such as a status code, headers, and, when appropriate, a response body.
- The client identifies the resource it wants.
- The client sends an HTTP request.
- The server receives and processes the request.
- The server returns an HTTP response.
- The client uses the response to display or process the requested resource.
This request-and-response model is also used beyond traditional webpages. HTTP can support APIs, automated applications, and communication between software systems.
What Is HTTPS?
HTTPS stands for Hypertext Transfer Protocol Secure. It uses HTTP together with TLS to protect communication between a client and a server.
TLS provides three important properties: confidentiality, integrity, and authentication. Encryption helps prevent unauthorized parties from reading information while it is being transmitted. Integrity protection helps detect unauthorized modification, while server authentication helps a browser establish that it is communicating with the server associated with the requested domain.
HTTPS therefore does not represent a completely different web protocol from HTTP. Instead, it describes HTTP communication carried through a TLS-secured connection.
How TLS Protects HTTPS Connections
Before protected HTTP communication begins, the client and server establish security parameters through a TLS handshake. The process involves negotiating cryptographic settings and establishing keys that can be used to protect subsequent communication.
Server authentication relies on a digital certificate and a chain of trust recognized by the client. Once the secure connection has been established, HTTP messages can travel through the protected channel.
HTTP And HTTPS Compared
The fundamental distinction is the protection applied to the communication channel. HTTP defines the exchange of HTTP messages, while HTTPS uses TLS to provide security for that exchange.
| Characteristic | HTTP | HTTPS |
|---|---|---|
| Meaning | Hypertext Transfer Protocol | Hypertext Transfer Protocol Secure |
| Communication | HTTP request and response | HTTP request and response protected by TLS |
| Encryption in transit | Not provided by HTTP itself | Provided through TLS |
| Integrity protection | Not provided by HTTP itself | Provided through TLS |
| Server authentication | Not provided by HTTP itself | Supported through TLS certificates and trust mechanisms |
| Typical URI scheme | http:// | https:// |
Why HTTPS Matters
Information sent through an unprotected connection can potentially be observed or altered by an attacker who can interfere with network traffic. HTTPS addresses this risk by protecting HTTP communication with TLS.
This protection is important whenever a connection carries information that should remain confidential or unchanged. It also helps establish the identity of the server through certificate-based authentication.
Modern web functionality increasingly depends on secure contexts. Browsers can restrict certain powerful web capabilities to pages delivered through secure connections, making HTTPS relevant not only to protecting data but also to the operation of modern websites.
What HTTPS Protects
- Confidentiality: TLS encrypts information while it travels between the communicating endpoints.
- Integrity: TLS helps detect unauthorized changes to transmitted information.
- Authentication: TLS enables the client to verify the identity associated with the server’s certificate.
HTTPS does not, however, make a website trustworthy in every respect. A site can use HTTPS and still contain inaccurate information, have insecure application logic, or be operated by someone with malicious intentions. HTTPS primarily protects the communication channel and authenticates the server according to the certificate trust system.
What Is The Difference Between HTTP And HTTPS In A URL?
The beginning of a web address is called its URI scheme. The http scheme identifies HTTP, while the https scheme identifies HTTP communication secured with TLS.
For example, an address beginning with https:// tells the browser that the requested resource must be accessed through a secured connection. For the HTTPS scheme, the standard default port associated with HTTP over TLS is 443.
The difference in the address is therefore more than a visual change. It tells the client which security requirements apply to communication with the requested origin.
How Websites Move From HTTP To HTTPS
A website can accept an HTTP request and redirect the client to the corresponding HTTPS address. A permanent redirect can help users who initially enter an HTTP address reach the protected version.
However, a redirect itself does not encrypt the initial HTTP request. If the first connection occurs through unprotected HTTP, an attacker able to interfere with that connection may attempt to alter the communication before the browser reaches HTTPS.
HTTP Strict Transport Security (HSTS) provides another mechanism. When a browser has received an appropriate HSTS policy over HTTPS, it can remember that the host should be accessed only through HTTPS for the specified period.
HTTP, HTTPS, And Modern Web Security
HTTP remains the foundation for exchanging web messages, while HTTPS adds transport security around that communication. The two concepts should therefore not be treated as competing protocols that perform entirely different jobs.
The practical distinction is straightforward: HTTP defines the communication, while HTTPS protects that communication with TLS. This separation also explains why improvements to HTTP and improvements to transport security can develop independently.
For users, the presence of HTTPS is an important security indicator, but it should be understood correctly. It indicates that the connection is protected and that the server has been authenticated according to the browser’s certificate trust process; it does not by itself guarantee that the website’s , business practices, or applications are safe.